Writing
AI proposes, engine proves: a handoff standard for chip design
published: 2026-09-27 · status: canonical · expanded from the original post
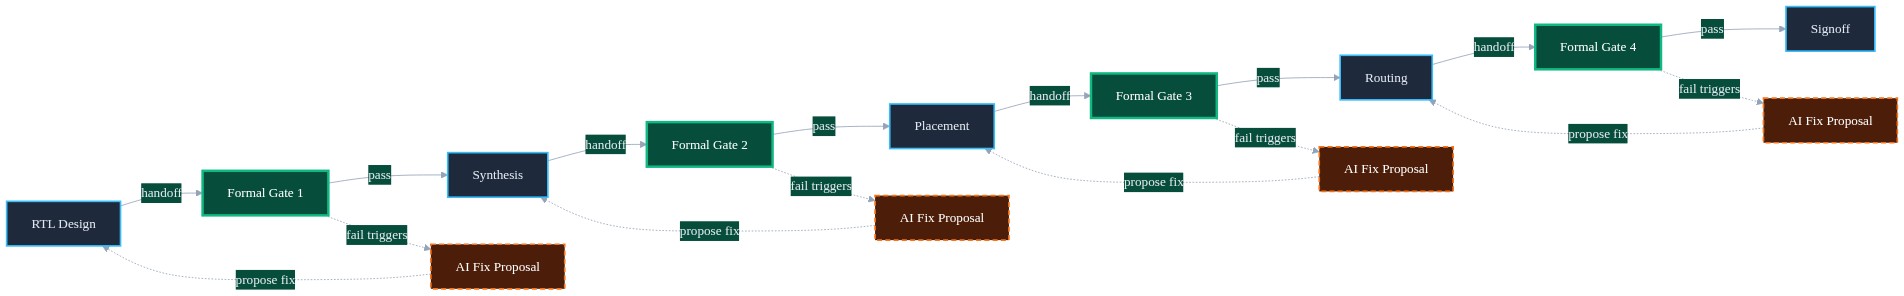
Chip design is full of handoffs. A design moves from architecture to RTL, from RTL to synthesis, from synthesis to place and route, and at each step the tool that produces the handoff has its own definition of 'done.' A synthesis tool might finish when timing under a specific corner is within bounds. Place and route might finish when routing congestion is below a threshold. Neither of those local definitions captures the intent that mattered upstream—why a latency target was set, why a buffer was sized, why an interface was frozen. That intent gets paraphrased, simplified, or dropped. Silent intent loss is one of the quiet reasons first-silicon success is hard to predict.
The case for AI as an intermediary
AI agents could sit at those boundaries. An agent could read the output of one tool, extract the design intent that is still represented there, and generate evidence that the next tool can consume. That evidence might explain what was constrained, what was relaxed, and what was assumed. If the handoff includes that kind of artifact, the next tool does not have to guess. Less intent is lost, and the design has a better chance of coming back from the fab behaving the way the team expected.
The case against
The problem with that picture is that an AI-generated assertion is a hypothesis, not proof. If an agent says 'this block meets the original latency spec,' that statement is not yet verification. If we let agents pass handoffs without independent, deterministic verification, we have not removed a black box; we have replaced one black box with another. Formal proofs and audit trails remain non-negotiable in chip design. But adding evidence checks at every boundary also has a real cost. It can slow the design cycle, and it can create false confidence if teams start treating generated evidence as checked evidence when it has not been checked.
What I'd do instead
I would treat AI outputs as proposals, not as completed handoffs. Before any proposal crosses a tool boundary, it should be checked against a formal engine. This is the same pattern software learned with inter-service handoffs. When two services talk, you do not trust that the payload is right because the producing team wrote a comment. You define a typed contract and run it through CI gates. The system checks the shape, the constraints, and the invariants automatically. Chip design needs the same discipline.
The artifacts that cross a chip design boundary should be machine-checkable. That means formal properties, golden models, deterministic checks—evidence artifacts that can be verified by tools, not by human judgment alone.
Not 'AI writes, human reviews,' but 'AI proposes, engine proves.'
This would not be free. Evidence checks at every boundary add latency, and the formal models have to be maintained. But the alternative is worse: letting agents generate plausible-looking handoffs and hoping the downstream tool will catch the problem later. That is how silent intent loss becomes a tapeout surprise.
Originally covered at semiengineering.com ↗