Writing
Enterprise copilots meet all three conditions for silent exfiltration
published: 2026-09-24 · status: canonical · expanded from the original post
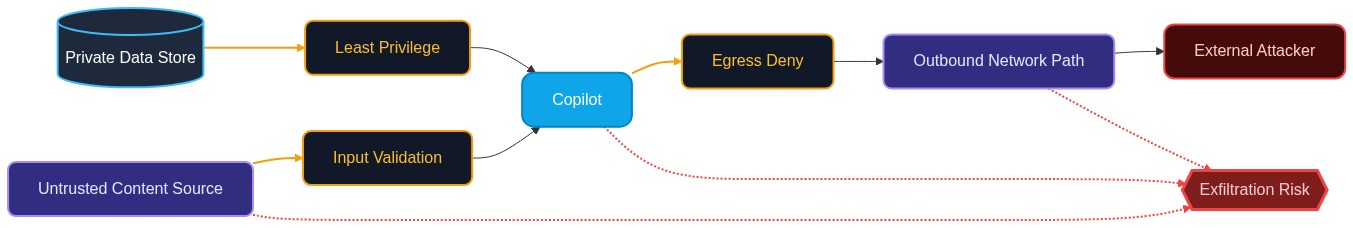
Enterprise copilots now meet all three conditions for silent data exfiltration: access to private data, untrusted content, and an outbound channel. That combination is what I call the lethal trifecta, and it is present in most production deployments today. Copilots are not just chat windows; they are agents that hold permissions on live data, process content from outside the trust boundary, and can make calls to external tools and services.
Private data is the target. Many enterprise copilots are granted broad read access to mailboxes, files, and calendars because that is what makes them useful. But broad access means the assistant can read things that no single user should be able to pull together in one place. If an attacker can influence the copilot, that access becomes an extraction surface.
Untrusted content is the trigger. Inbound email, public forms, and documents from partners or customers all arrive from outside the trust boundary. They can contain hidden instructions, malformed content, or malicious payloads. When a copilot processes that content while holding enterprise permissions, the boundary between untrusted input and privileged action disappears.
The outbound channel is what turns influence into exfiltration. Copilots often have the ability to make web requests, call APIs, send email, or read from external sources. Once private data can be folded into a response and sent somewhere outside your control, you have a leak that may look like legitimate assistant behavior.
The "silent" part matters because there is no loud exploit or malware beacon. The assistant is supposed to read data, process messages, and call tools. When an attacker abuses those same capabilities, the activity blends into normal use. Logs may show a copilot reading a mailbox and posting to an API, but that can look identical to a legitimate workflow.
- Scope copilot access to least privilege, not your whole tenant.
- Treat inbound email and public forms as untrusted input vectors.
- Restrict outbound calls from copilot contexts; default deny.
- Map for the lethal trifecta: private data + untrusted input + egress.
These are not detection mechanisms. Structural controls beat classifiers. A classifier has to recognize a malicious payload, and attackers only need to be right once. A default-deny egress rule removes the path entirely. If the copilot cannot call outward, it cannot exfiltrate, no matter how clever the prompt injection is.
No egress, no exfiltration.
Mapping for the lethal trifecta is a useful audit exercise. For each copilot or agent, ask what private data it can read, what untrusted content it processes, and what outbound channels are reachable from its context. If all three conditions are present, treat it as a high-risk integration until the egress path is closed.
The reason these controls matter more than filtering is that they address the preconditions directly. A classifier may catch a known attack pattern, but it will not close the path. Scope limits reduce what is exposed, untrusted-input treatment reduces what an attacker can influence, and egress denial removes the channel that turns influence into loss.
The documented EchoLeak and ForcedLeak cases show this is not theoretical. Those examples, detailed in 'The Lethal Trifecta in Production,' demonstrate how these paths combine in practice. The fix is not to trust better prompts or smarter filters. The fix is to design the environment so the exfiltration path does not exist.
Originally covered at aminrj.com ↗